What Is HSTS? Understanding Your Website’s Missing Security Header
TL;DR: HSTS tells browsers to keep using HTTPS when connecting to your website. If your website report flags a missing HSTS header, your site may still have a working SSL certificate, but it is missing an additional layer of connection protection. Your hosting provider or web developer can help configure and verify it.
You run a website check/scan and see this finding: “Missing HTTP Strict Transport Security (HSTS).”
It sounds technical. You might also wonder why it matters when your website already uses HTTPS.
HSTS helps browsers remember that your website should only be accessed through a secure connection. Understanding this setting can help you have a more productive conversation with the person who manages your website.
What Is HSTS?
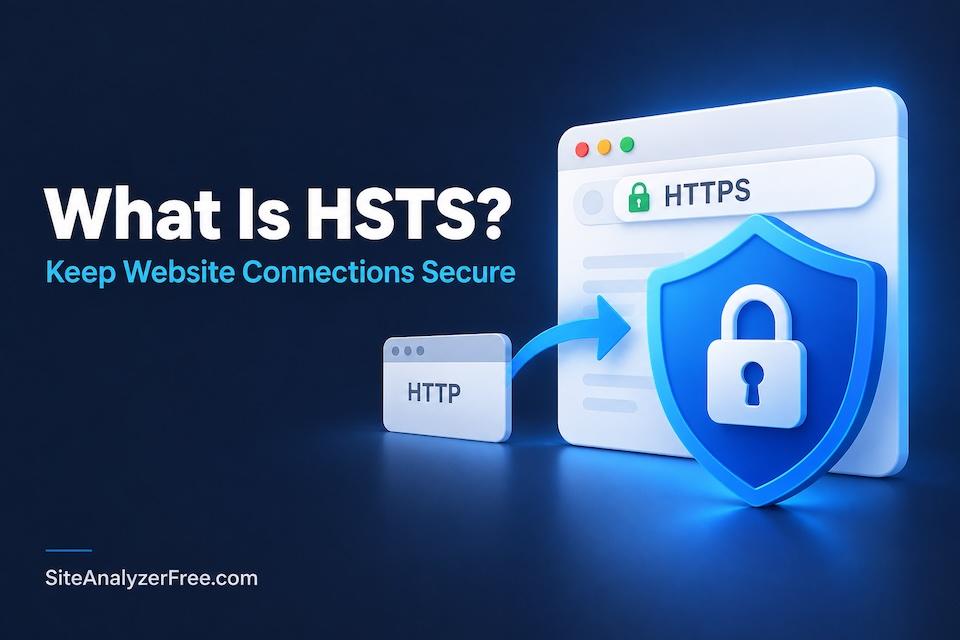
HSTS stands for HTTP Strict Transport Security.
Your website sends the browser a small instruction called the Strict-Transport-Security response header. After receiving it over HTTPS, the browser remembers to use HTTPS for future connections during the policy’s lifetime—even when someone follows an HTTP link.
This instruction is delivered behind the scenes. It does not change your website’s appearance. MDN explains how the HSTS header works.
Why Does It Matter?
An insecure HTTP connection can give an attacker on the network an opportunity to intercept or modify traffic.
HSTS helps prevent attempts to keep a visitor on HTTP when HTTPS is available. This type of downgrade is often called SSL stripping. It also helps reduce opportunities to intercept or manipulate cookies through insecure connections.
These protections are useful for websites handling logins, customer accounts, and other sensitive interactions. HSTS is one part of protecting visitors; it does not replace other website security measures. Read OWASP’s HSTS guidance.
Isn’t an HTTPS Redirect Enough?
An HTTPS redirect tells a browser where to go after an HTTP request reaches the server.
With an active HSTS policy, the browser upgrades the request before sending it over HTTP. That removes an insecure step.
There is a first-visit limitation: the browser ordinarily needs to receive the policy through a successful HTTPS connection before it can remember it. MDN covers redirects and this initial-connection limitation.
What Does “Missing HSTS” Mean in Your Report?
When SiteAnalyzerFree.com reports that the header was not found, it means the checked response did not include that instruction.
It does not establish that your website has been hacked or that HTTPS is broken. It identifies a configuration item worth reviewing.
The next step is to have your developer check the response headers and confirm where the setting belongs in your hosting setup.
How Do You Fix a Missing HSTS Header?
Ask your hosting provider or developer to review the finding and plan the change.
This is more on your website host to fix/change than your developer, actually. Sometimes your host and developer are the same company (this is best usually so you have just one place to call instead of being the middleman between the two).
A careful rollout should include:
- Checking HTTPS first. Confirm the website works reliably through secure connections.
- Reviewing subdomains. Before applying the policy to subdomains, check services such as your shop, customer portal, and internal tools.
- Starting with a short policy duration. Test before asking browsers to remember the setting for longer periods.
- Monitoring and extending the policy. Increase the duration gradually after confirming everything works.
The HSTS deployment guidance recommends a staged rollout so problems can be caught early. See the deployment recommendations.
What Do the HSTS Settings Mean?
You may see your developer refer to these settings:
max-age: How many seconds the browser should remember the policy.includeSubDomains: Extends the policy to subdomains.
An active policy also prevents visitors from bypassing certain certificate errors. Keeping certificates valid remains essential. See MDN’s header reference.
You may also encounter preloading, which puts a domain on a list browsers can consult before a first visit. This is a separate commitment. The preload service currently recommends HSTS but advises against preloading as a general recommendation, and removal can take months. It should not be enabled casually. Read the preload guidance.
What Should You Expect After the Fix?
The intended outcome is stronger enforcement of secure browser connections.
Your developer should verify that the expected header appears on HTTPS responses, then rerun the website analysis. Keep the finding and the follow-up result together so you have a record of what changed.
If you need help interpreting the report or arranging the work, our preferred vendor, Webstix, can help review the next steps.
Visit SiteAnalyzerFree.com to check your website for HSTS (check #46) and discover which other improvements deserve attention.